
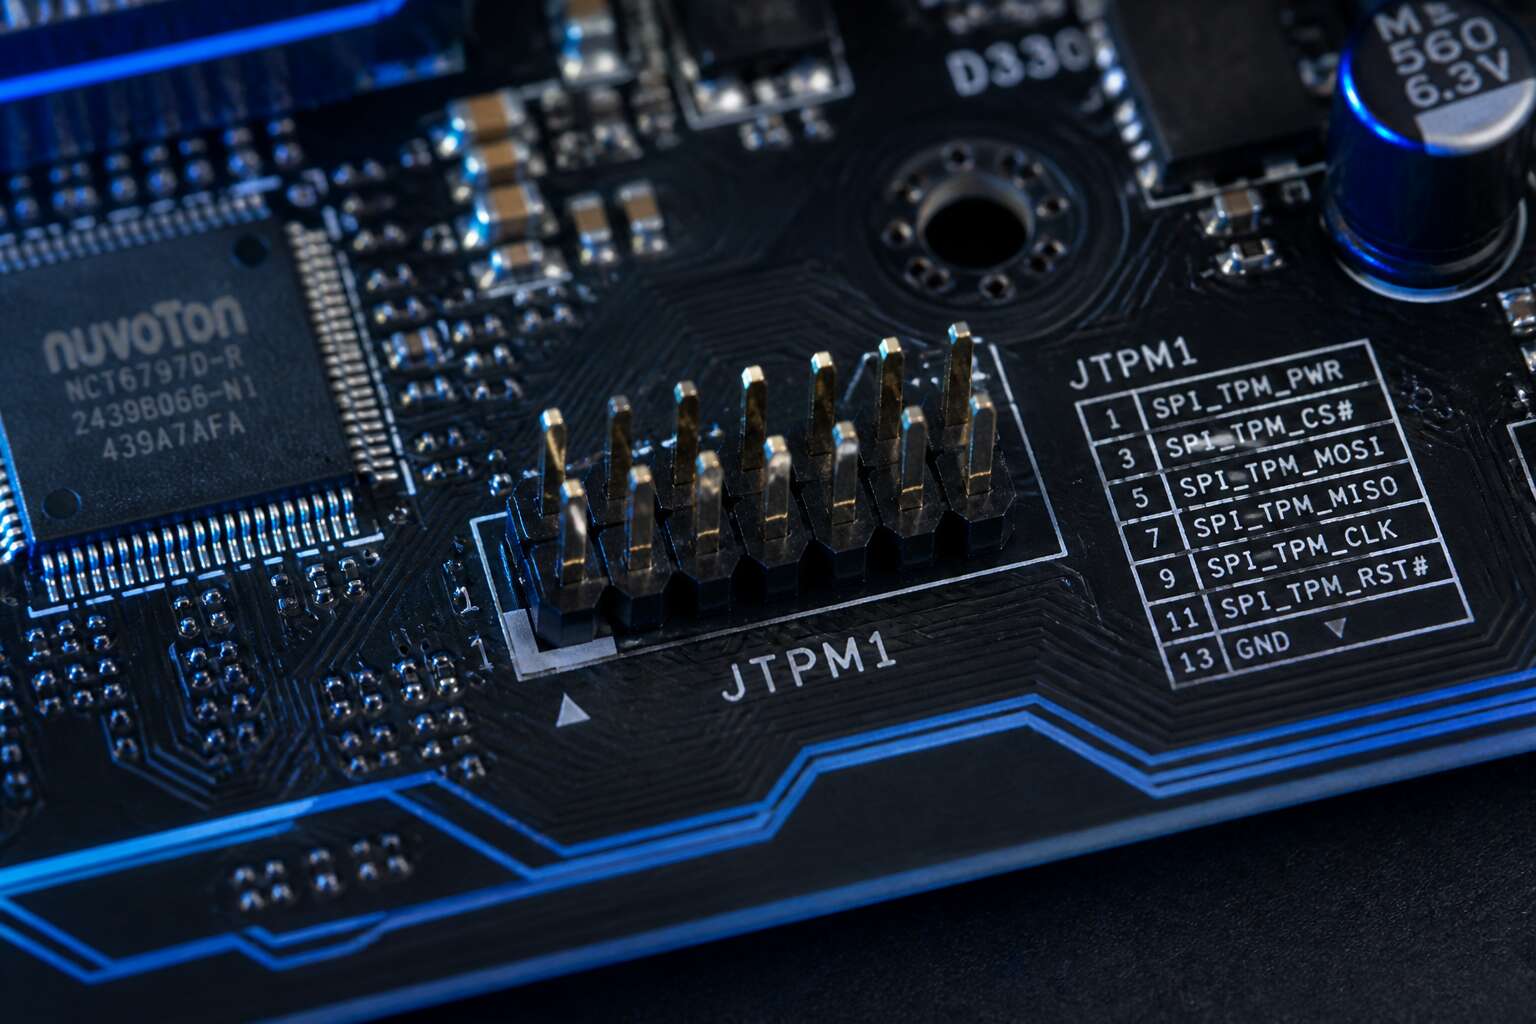
Understanding the TPM Header on Motherboards
The TPM header rarely gets attention. When Windows 11 mandated TPM 2.0, millions of users suddenly cared about this socket. The motherboard jtpm1 changes how we approach that requirement. It gives you a direct line to hardware-backed encryption, without hunting for a separate module.
I have looked at this closely. The header sits near the chipset and links to the firmware’s fTPM or a physical dTPM module. That distinction matters because physical modules offer a different tamper profile. The pinout compatibility is often the deciding factor!
- Whether the header supports your chosen module’s pinout
- If the BIOS has a clear fTPM fallback option
- How the manufacturer labels the header on the board itself
The motherboard jtpm1 integrates these details into a straightforward layout. Short pins, clear markings, and proper firmware support make all the difference.
JTPM1 Pinout and Signal Definitions
Twenty pins sit on the JTPM1 header of your motherboard jtpm1, yet most users cannot name more than three. This 20 pin connector carries trust and security, but manuals rarely explain its signals. Let me decode the essentials for you.
The pinout follows a clear order, once you spot the pattern. Here are the critical pins:
- Pin 1 supplies +3.3V standby power.
- Pin 3 carries the CLK clock signal for the trusted platform module.
- Pin 7 handles the LPC reset line for the controller.
Each signal matters. Ground pins sit between them, preventing electrical noise. This connector routes these lines to the TPM chip, which then validates your system’s integrity. Respect the pinout, and your security features will shine!
Compatibility and Installation Considerations
The motherboard jtpm1 header often remains unoccupied, a quiet socket waiting for the Trusted Platform Module that can seal your system’s secrets. A 2024 industry report found that nearly 70% of users never install a TPM, leaving their encryption keys exposed. Before you seat that module, check your BIOS version; older firmware may not recognize the hardware. Ensure your operating system supports TPM 2.0, especially if you run Windows 11.
Consider these steps for a clean installation:
1. Power down and disconnect all cables.
2. Locate the jtpm1 pins near the edge of the board.
3. Align the module’s notch with pin 1, then press firmly.
After booting, enter UEFI and enable the TPM device. Compatibility with your motherboard jtpm1 also demands a matching connector type, as some boards use a 2×8 layout instead of the standard 2×6. Verify your model against the vendor’s manual, and you will avoid a frustrating evening of unmatched pins and dead diagnostics.
Troubleshooting and Common Issues
Why does a motherboard JTPM1 header cause so much grey hair? Because it works beautifully until the exact moment you need it for Windows 11, and then it vanishes like a R1 coin in a vending machine.
The most common gremlin is the BIOS setting. If the TPM shows as “No Device”, you are probably looking at the wrong firmware toggle. Disable Intel PTT or AMD fTPM, save, and reboot. Then, power down completely and reseat the module.
Here is the quick fix sequence:
- Update your BIOS to the latest stable build.
- Clear the CMOS using the jumper pins.
- Uninstall the TPM driver from Device Manager.
If the motherboard JTPM1 still refuses to play nicely, check your physical connection. A loose pin or a speck of dust is usually the culprit. And if all else fails, remember that the TPM is a security chip, not a dam that holds back data. You won’t lose your files, just your ability to encrypt new ones temporarily. Stay calm, grab coffee, and retrace your steps.
BIOS and Software Configuration
There is a peculiar silence when the motherboard jtpm1 first powers on. The BIOS screen, a pale ghost, waits for your command. I have spent hours in that cold light, configuring trust and security in equal measure. The firmware holds secrets that most users never bother to unlock.
For the uninitiated, the navigation on the motherboard jtpm1 can feel like a labyrinth. But the essentials are straightforward:
- Enable TPM 2.0 in the Security tab, or the operating system will refuse to play.
- Set the boot order to UEFI only, not legacy, to avoid compatibility ghosts.
- Update the firmware before installing any critical drivers.
These small choices dictate everything downstream. A poorly configured BIOS here in Johannesburg can corrupt an entire Windows deployment. The software side is equally demanding. You must pair the chipset drivers with the exact firmware revision, or the system will stutter. Trust me, I have seen the blue screens that follow.
0 Comments